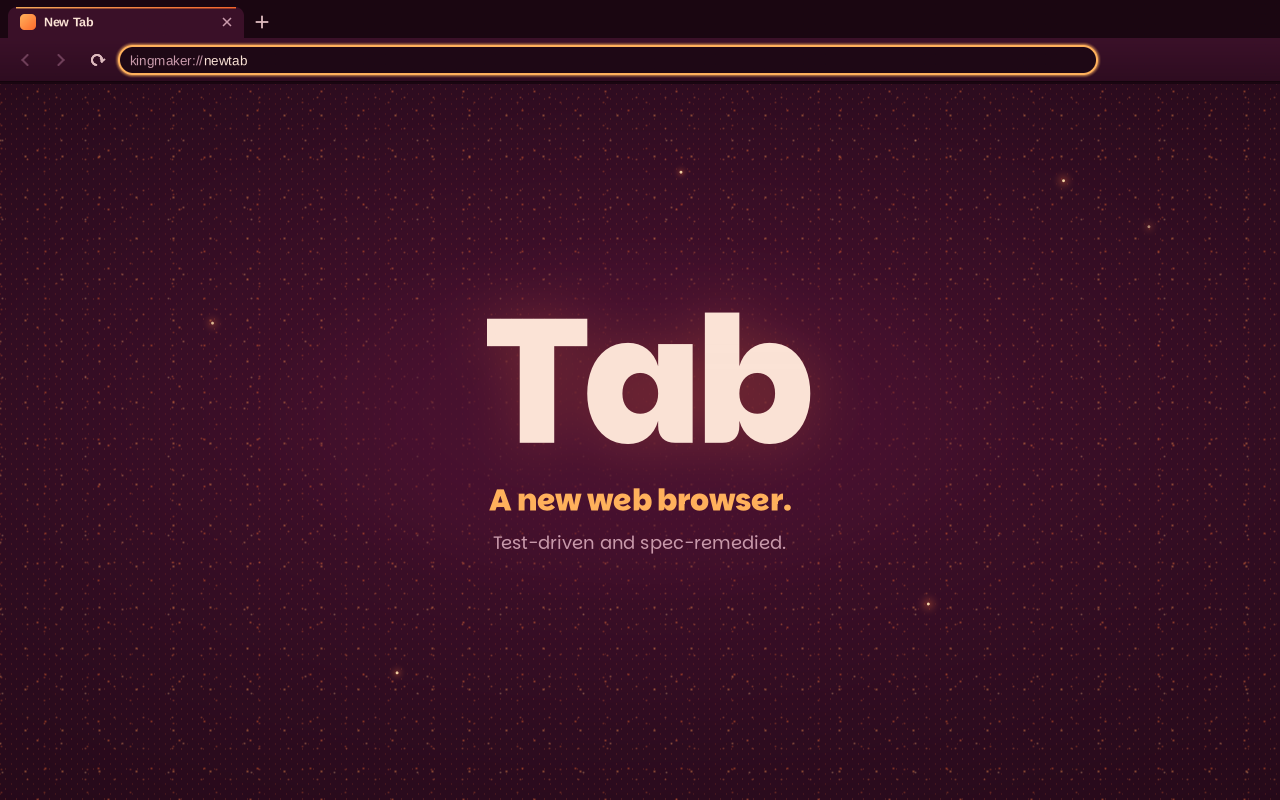
A pre-release build of Tab on Linux. The screenshots are unedited, and the engine drawing these pages is the one the tests below measure.
Web standards test results
No Chromium, WebKit or Gecko underneath: Tab's engine is new, test-driven and spec-remedied. It passes 1,774,103 of 1,912,797 tests across five upstream suites.
Build 0.1.2681, measured October 26, 2026. Saved with the page; newer results may exist.
- Test262 97.85% 95,931 of 98,040
- WPT testharness 92.06% 1,459,574 of 1,585,538
- WPT rendering 88.98% 27,483 of 30,888
- WPT remaining compatibility 87.91% 52,494 of 59,710
- WebAssembly spec 100% 138,621 of 138,621
One developer architects the engine, builds the test pipelines, checks every result and calls out anything that doesn't hold up. AI agents, mostly Claude and GPT, write most of the code. The web's own test suites decide what's done.
Full upstream catalogs, nothing filtered; one row per test case/subtest; only PASS counts as a pass. Raw results
Security, so far
About 70% of serious security bugs in Chrome are memory-safety bugs, by Chromium's own count. Writing Tab in Rust takes most of those off the table. The other 30% are logic: which site may read what, and when. That part is real work, built into the engine and tested side by side with Chromium with every request on the wire recorded. Here is where it stands.
In place
- Sites can't read each other's data: cross-origin checks on fetch, XHR, redirects and preflights.
- Cookies follow HttpOnly and SameSite, across frames and redirects.
- Cross-origin images, fonts and frames can't leak through canvas, element capture or Location.
- One site's cached response is never served to another.
- Referrer Policy, Mixed Content blocking and Upgrade Insecure Requests.
- Subresource Integrity and Trusted Types.
Still open
- No operating-system sandbox yet: the browser runs as a single process.
- Content Security Policy is only partly enforced.
- No independent security review yet.
34 security findings logged so far, each with its fix or the reason for a decision; 26 are fully fixed. Record as of October 26, 2026.